Managing servers and applications manually becomes increasingly difficult as infrastructure grows. Inconsistent configurations, time-consuming updates, and configuration drift can lead to errors, downtime, and higher operational overhead. Puppet helps solve these challenges by automating infrastructure configuration and enforcing consistent system states across environments.
This article explains what Puppet is, how it works, its key features, common use cases, and the benefits and limitations of using it for infrastructure automation.
What Is Puppet?
Puppet is an infrastructure automation and configuration management platform that helps organizations provision, configure, and maintain servers and other IT resources at scale. It uses infrastructure as code (IaC) principles, allowing administrators to define the desired state of systems in code. Puppet then continuously enforces these configurations, helping keep systems consistent. It also reduces manual effort, and minimizes configuration drift across physical, virtual, cloud, and hybrid environments.
Learn more about server provisioning and how automated methods like configuration management compare to manual and image-based approaches.
How Does Puppet Work?
Puppet automates infrastructure management by combining a client-server architecture with reusable configuration code. Instead of configuring each system individually, administrators define the desired state of their infrastructure, and Puppet continuously ensures that managed systems remain compliant with those definitions.
Puppet Architecture
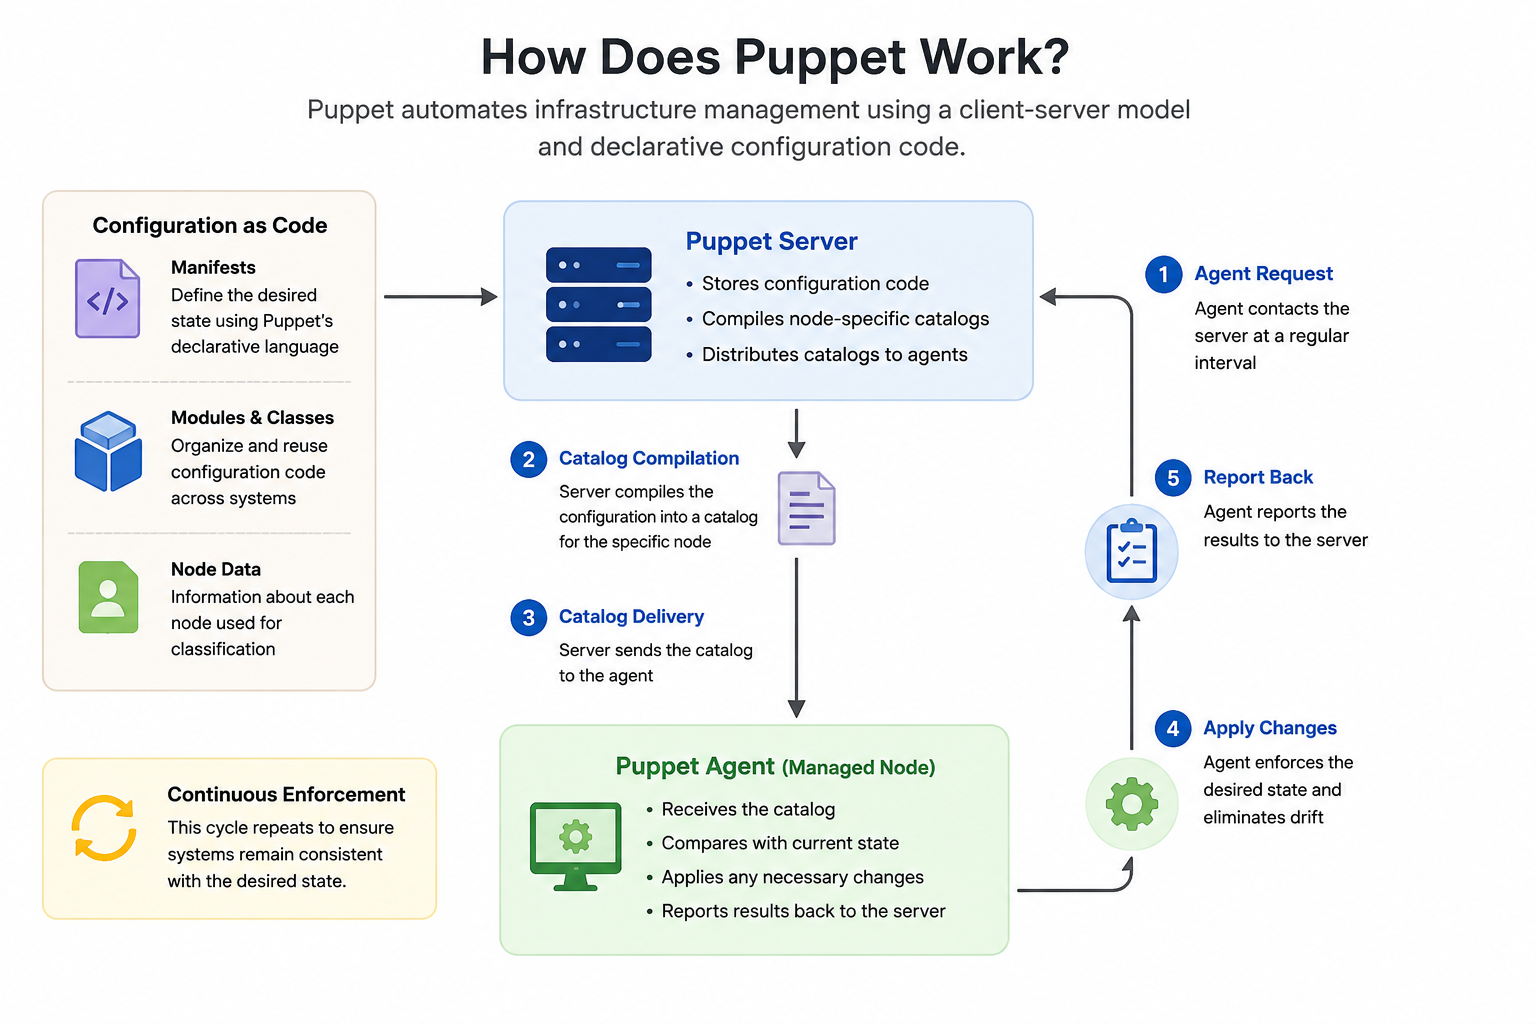
Puppet consists of a Puppet server and one or more Puppet agents. The Puppet server stores configuration code, compiles node-specific catalogs, and distributes them to managed systems. Each managed node runs a Puppet agent that periodically communicates with the server, retrieves its assigned catalog, applies any required changes, and reports the results.
Although Puppet is primarily designed as an agent-based platform, it also supports agentless task execution through Puppet Bolt, which runs ad hoc commands and tasks over SSH or WinRM without requiring an installed agent.
Puppet Manifest and Declarative Language
Puppet configurations are written as manifests using Puppet's declarative language. Rather than specifying every command needed to configure a system, administrators describe the desired end state, such as which packages should be installed, which services should be running, or how configuration files should be managed. Puppet determines the actions required to achieve that state, making configurations easier to write, maintain, and reuse.
Puppet Modules and Classes
To organize configuration code, Puppet groups related resources into modules and classes. A module is a self-contained collection of manifests, templates, files, and supporting data that manages a specific application or service, such as Apache, NGINX, or MySQL. Within a module, classes define reusable configuration logic that can be assigned to one or many systems, allowing administrators to apply standardized configurations consistently across large environments.
Puppet Catalog Compilation and Enforcement
When a Puppet agent contacts the Puppet server, the server combines the relevant manifests, modules, classes, and node-specific data into a catalog. The catalog defines the exact resources and configurations that the node should have. After receiving the catalog, the Puppet agent compares it with the system's current state, applies any necessary changes to eliminate configuration drift, and reports the outcome to the server. This continuous enforcement helps keep infrastructure consistent even as systems change over time.
Key Features of Puppet
Puppet includes a range of features that simplify infrastructure automation, improve configuration consistency, and make it easier to manage systems at scale. The following capabilities are among its most important features:
- Declarative configuration management. Puppet uses a declarative language that lets administrators define the desired state of infrastructure instead of writing procedural scripts, making configurations easier to read and maintain.
- Idempotency. Puppet only applies changes when a system differs from its desired state. Repeated runs produce the same result without making unnecessary modifications, ensuring consistent and predictable configurations.
- Infrastructure as code. Infrastructure configurations are stored as code, making them version-controlled, reusable, and easier to test and maintain.
- Cross-platform support. Puppet manages a wide range of operating systems, including Linux, Windows, and UNIX-based platforms, allowing organizations to automate heterogeneous environments from a single framework.
- Modular architecture. Puppet organizes configuration code into reusable modules and classes, making it easier to standardize deployments and share configurations across multiple systems.
- Puppet Forge. Puppet Forge is a public repository of community-maintained and vendor-supported modules that administrators can use to deploy and manage common applications and services without building configurations from scratch.
- Continuous configuration enforcement. Puppet regularly checks managed systems for configuration drift and automatically restores them to their defined state when changes are detected.
- Node classification. Administrators can assign different configurations to servers based on their role, environment, operating system, or other attributes, enabling centralized management of diverse infrastructure.
- Reporting and auditing. Puppet generates detailed reports showing configuration changes, compliance status, and execution results, helping administrators monitor infrastructure and troubleshoot issues.
Together, these features make Puppet a scalable and reliable platform for automating configuration management across physical, virtual, cloud, and hybrid environments.
Puppet vs. Other Configuration Management Tools
Puppet is one of several popular infrastructure automation tools, but each solution is designed for different goals and workflows. Understanding their strengths helps organizations choose the right tool for their environment.
Puppet vs. Ansible
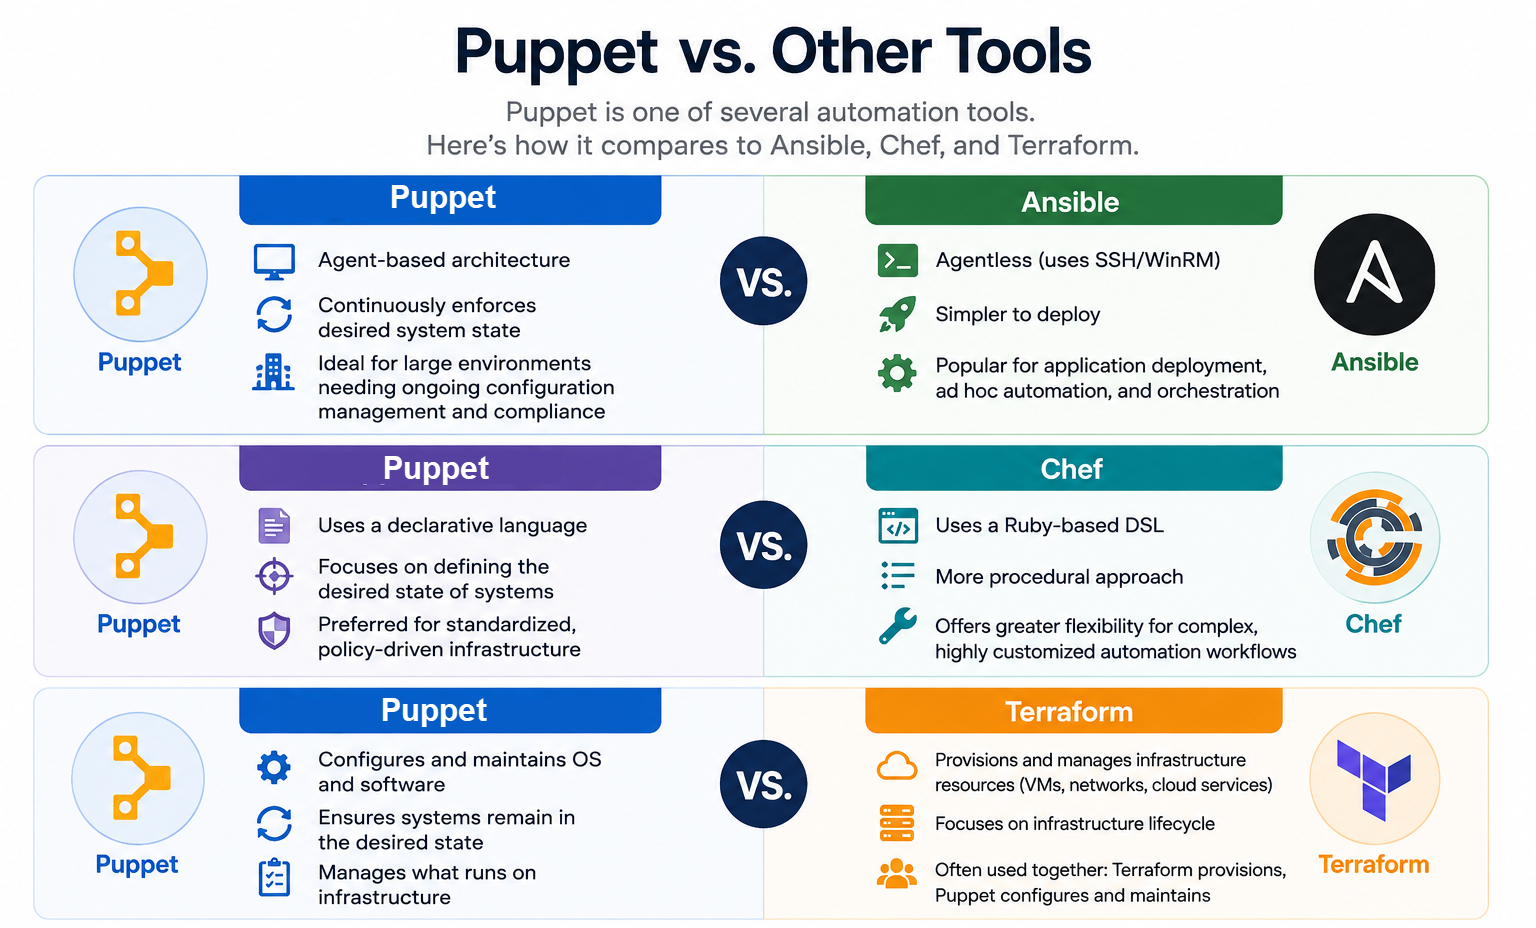
Puppet uses an agent-based architecture and continuously enforces the desired system state, making it well suited for large environments that require ongoing configuration management and compliance. Ansible is primarily agentless and executes tasks over SSH or WinRM, making it simpler to deploy and a popular choice for application deployment, ad hoc automation, and orchestration.
Learn more about how Ansible fits with different tools in our articles on Ansible vs. Terraform and Ansible vs. Chef.
Puppet vs. Chef
Both Puppet and Chef provide configuration management and support infrastructure as code, but they take different approaches. Puppet uses a declarative language that focuses on defining the desired state of systems, while Chef uses a Ruby-based domain-specific language (DSL) that follows a more procedural approach. Policy-driven infrastructure thrives with Puppet, whereas Chef offers greater flexibility for complex, highly customized automation workflows.
Puppet vs. Terraform
Although Puppet and Terraform both support infrastructure as code, they solve different problems. Terraform focuses on provisioning and managing infrastructure resources, such as virtual machines, networks, and cloud services, while Puppet configures and maintains the operating systems and software running on those resources after they are deployed. Many organizations use Terraform to provision infrastructure and Puppet to configure and maintain the operating systems and software running on that infrastructure.
Puppet Benefits
Organizations use Puppet to improve the efficiency, reliability, and maintainability of their IT infrastructure. They do so by automating configuration management and enforcing consistent system states. These advantages make it easier to manage growing environments while reducing operational risk:
- Improves operational efficiency. By automating repetitive configuration and maintenance tasks, Puppet reduces manual administration, speeds up routine operations, and allows IT teams to focus on higher-value work.
- Enhances reliability. Puppet continuously enforces the desired system state, reducing configuration errors and helping ensure that servers and applications remain stable over time.
- Maintains configuration consistency. Standardized configurations are applied across all managed systems, minimizing configuration drift and ensuring environments remain predictable regardless of scale.
- Simplifies infrastructure maintenance. Reusable modules, centralized configuration management, and infrastructure-as-code practices make environments easier to update, troubleshoot, and maintain throughout their lifecycle.
- Supports security and compliance. Puppet helps organizations consistently apply security policies and configuration standards while providing reporting capabilities that simplify compliance monitoring and auditing.
- Scales with infrastructure growth. Whether managing dozens or thousands of systems, Puppet enables administrators to maintain consistent configurations through centralized automation.
- Improves change management. Configuration changes are defined as code, making them easier to review, version, test, and deploy consistently across environments.
Together, these benefits help organizations build more efficient, reliable, and maintainable infrastructure while simplifying long-term operations.
Puppet Use Cases
Puppet’s flexibility makes it suitable for organizations managing everything from a handful of servers to large-scale enterprise infrastructure, including:
- Server configuration management. Puppet automates the installation and configuration of operating systems, packages, services, users, and files to ensure consistent server configuration.
- Configuration drift remediation. By continuously comparing systems against their desired state, Puppet automatically detects and corrects unauthorized or unintended configuration changes.
- Application deployment. Puppet deploys and configures applications and their dependencies consistently across development, testing, and production environments.
- Infrastructure provisioning workflows. Puppet configures newly provisioned infrastructure after deployment, preparing servers for production by installing software and applying standard configurations.
- Compliance enforcement. Organizations use Puppet to apply security policies, configuration standards, and access controls consistently across managed systems while generating reports for auditing purposes.
- Patch and software management. Puppet automates software installation, updates, and package version management, helping maintain secure and up-to-date systems.
- Cloud and hybrid infrastructure management. Puppet manages configurations across on-premises servers, public cloud platforms, virtual machines, and hybrid environments using the same automation framework.
- DevOps and CI/CD integration. Puppet integrates with DevOps pipelines to automate environment configuration and ensure consistent infrastructure throughout the software delivery lifecycle.
These use cases demonstrate how Puppet simplifies infrastructure management by automating repetitive tasks, enforcing consistency, and supporting reliable operations across diverse IT environments.
Getting Started with Puppet
Starting with Puppet involves installing the components and creating a simple manifest that defines the state of a system. Once these basics are in place, you can begin automating configuration management across your infrastructure.
Installing Puppet
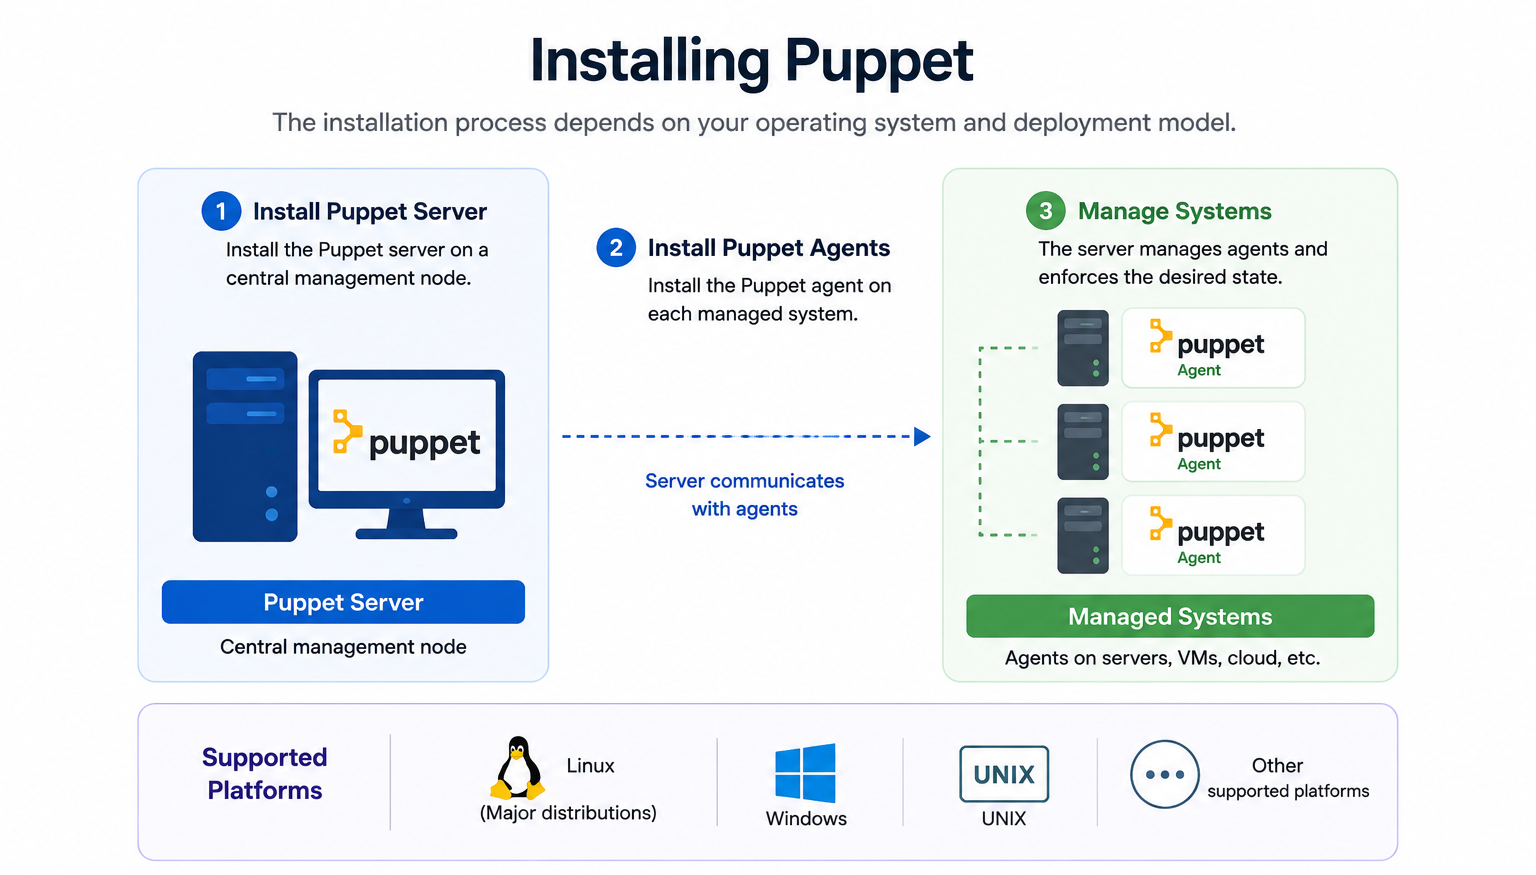
The installation process depends on your operating system and deployment model. In a typical setup, you install the Puppet server on a central management node. Then, you install the Puppet agent on each managed system. Puppet packages are available for most major Linux distributions, Windows, and other supported platforms.
For detailed installation instructions, refer to our guides on how to install Puppet on Ubuntu and how to install Puppet on macOS.
Writing Your First Puppet Manifest
A Puppet manifest is a text file that defines the desired configuration of a system. The following example ensures that the nginx package is installed and that the nginx service is running and starts automatically after boot.
package { 'nginx':

  ensure => installed,

}

service { 'nginx':

  ensure  => running,

  enable  => true,

  require => Package['nginx'],

}
Save the manifest as a .pp file and apply it using the puppet apply command. Puppet compares the current system configuration with the manifest and makes only the changes needed to achieve the defined state.
Puppet Challenges
While Puppet is a powerful configuration management platform, it also has limitations that organizations should consider before adopting it. Understanding these challenges helps determine whether Puppet is the right fit for your infrastructure and operational requirements:
- Steeper learning curve. Puppet's declarative language, architecture, and concepts such as manifests, modules, catalogs, and classes require time to learn, particularly for teams new to infrastructure automation.
- Agent management overhead. Most Puppet deployments rely on agents installed on managed nodes, which introduces additional components that must be deployed, monitored, and maintained.
- Infrastructure complexity. Large Puppet environments may require dedicated Puppet servers, certificate management, and careful planning to ensure scalability and high availability.
- Slower change propagation. Because Puppet agents typically run at scheduled intervals, configuration changes may not be applied immediately unless a run is triggered manually.
- Module quality varies. Although Puppet Forge provides thousands of reusable modules, their quality, maintenance, and compatibility can differ, making it important to evaluate modules before deploying them in production.
- Debugging can be challenging. Troubleshooting configuration errors or complex module dependencies can be difficult, especially in large environments with many interconnected resources.
- Less suited for ad hoc automation. Puppet maintains long-term system state rather than executing one-time administrative tasks, where agentless tools may be more convenient.
Despite these challenges, Puppet remains a strong choice for organizations that need scalable, policy-driven configuration management and continuous enforcement of system configurations.
Puppet Enterprise vs. Open-Source Puppet
Open-source Puppet has traditionally provided the core configuration management functionality needed to automate infrastructure, including manifests, modules, catalogs, and agent-based configuration enforcement, while Puppet Enterprise builds on these capabilities with a web-based management console, role-based access control (RBAC), orchestration tools, reporting and compliance dashboards, integrated certificate management, and commercial support.
Since 2025, however, Puppet's owner, Perforce, has restructured how the open-source edition is distributed. New Puppet binaries and packages are now published to a private repository rather than public channels, and access requires accepting an End-User License Agreement (EULA). Use is free for deployments of up to 25 nodes, while larger deployments require a paid Puppet Labs Support Commercial License. The underlying code remains Apache 2.0-licensed, but the change reduced public visibility into ongoing development.
In response, the Puppet open-source community, led by Vox Pupuli, forked the project into OpenVox, an independently maintained, fully open continuation of Puppet under the same Apache 2.0 license.
Organizations evaluating Puppet today generally choose between Puppet Enterprise for centralized management and vendor support, the EULA-gated open-source edition for small deployments, or OpenVox for teams that want to stay on a community-governed, openly developed codebase.
Puppet FAQ
Here are the answers to the most commonly asked questions about Puppet.
Is Puppet Still Relevant?
Yes. Although newer infrastructure automation tools such as Ansible and Terraform have become widely adopted, Puppet remains a relevant and widely used configuration management platform, particularly in large enterprise environments. Its strengths in declarative configuration management, continuous state enforcement, compliance, and large-scale infrastructure management make it well suited for organizations that need consistent, policy-driven system administration.
What Language Does Puppet Use?
Puppet uses its own declarative DSL to define the desired state of infrastructure. Instead of writing step-by-step instructions, administrators describe how system configuration should go. Puppet determines the actions needed to achieve that state. The language is designed specifically for configuration management. Also, it supports reusable components such as manifests, classes, and modules, making it easier to automate and maintain infrastructure at scale.
Is Puppet Free to Use?
Partially. Open-source Puppet remains free to use for smaller deployments, but since 2025 it has been distributed under an End-User License Agreement (EULA). This license caps free use at 25 nodes. Larger deployments require a paid commercial license. Organizations that want a fully open, community-governed alternative can instead use OpenVox. It is maintained independently under the Apache 2.0 license with no such usage cap.
Why Organizations Continue to Use Puppet
Puppet is a mature and proven configuration management platform. It helps organizations automate infrastructure, enforce consistent system configurations, and reduce manual administration. Its declarative approach, reusable modules, and continuous state enforcement make it well-suited for managing large-scale on-premises, cloud, and hybrid environments. Puppet enables organizations to automate repetitive configuration tasks, maintain consistency, and manage infrastructure more efficiently.